Targeting Democracy
Pegasus and Mercenary Spyware Attacks on Serbian Pro-Democracy Figures
In collaboration with the SHARE Foundation, we found with high confidence that Professor Vladan Đokić, Rector of the University of Belgrade, and prominent supporter of the Serbian student movement, was hacked with NSO Group’s Pegasus spyware in 2026. Additionally, we note that Rade Bajić, who, as a prosecutor, investigated official corruption in a failed project in Belgrade, received an Apple Threat Notification. These notifications are high-confidence indicators of targeting with mercenary spyware such as Pegasus. Our investigations into these cases are ongoing.
Background: Recent Spyware Attacks in Serbia
Serbia’s student-led pro-democracy movement, born from the November 2024 anti-corruption protests, has faced widespread targeting with spyware as part of broader state repression. In 2026 alone, investigations led by the SHARE foundation with the support of the Citizen Lab and Amnesty International’s Security Lab found that at least 14 people were targeted with advanced spyware. The targets included members of the protest movement, activists, and opposition party members. SHARE has noted that the timing of those cases coincided with the run-up to Serbia’s March 29, 2026 local elections.
Our forensic findings from that investigation included the discovery that NSO Group’s Pegasus spyware was used to hack the phone of a student protester. Amnesty’s Security Lab found repeated use of homegrown Serbian government spyware by the authorities against protesters.
This research note reveals two newly-discovered cases, raising the total to at least 16 members of civil society in Serbia publicly known to have been targeted or infected with mercenary spyware.
Vladan Đokić, Rector of University of Belgrade, infected with Pegasus Spyware
Professor Vladan Đokić is the Rector of the University of Belgrade and a strong supporter of Serbian students’ ongoing pro-democracy campaign. He is famous for refusing to facilitate a government-led crackdown on student protesters, which led to intense pressure from the Serbian authorities. On March 31, 2026, Serbian authorities raided his offices, and reportedly seized computers and servers. Until September, he was frequently mentioned as a potential head of the Student List for Serbia’s upcoming October 25th, 2026 snap parliamentary elections. He has been extensively targeted by attacks in pro-government media.
Technical analysis of artifacts from Vladan Đokić’s iPhone
With the assistance of the SHARE Foundation, the Citizen Lab analyzed forensic artifacts collected from Vladan Đokić’s Apple iPhone at his request and with his consent. We found with high confidence that it was infected with NSO Group’s Pegasus spyware in 2026. The infection leveraged a zero-click exploit. No action, such as a click or opening a file was necessary for infection. Our investigation into this case is ongoing.
Rade Bajić: Apple Threat Notification Recipient
Rade Bajić was a senior prosecutorial associate at Serbia’s Public Prosecutor’s Office for Organized Crime (TOK) in Belgrade. He is best known for his work on a corruption investigation into a failed “Trump Tower” project in Belgrade, Serbia. The project was set to be built on the ruins of a previously-declared protected cultural heritage site. Reportedly, Serbia’s then-president personally intervened to demand removal of the site’s protected status and allow the project to go forward.
In 2024, prosecutors opened an investigation into the case, following an anonymous complaint alleging public corruption. Bajić, who worked on the investigation, referred to as the “Generalštab” case, states that he was removed from the case in November 2025 without explanation. In February 2026, Bajić spoke out at a demonstration, denouncing political interference in the case, and other abuses of power.
Mr Bajić was sent an Apple Threat Notification on August 13th, 2026, as well as a reminder message on August 27th, 2026 (Figure 1).
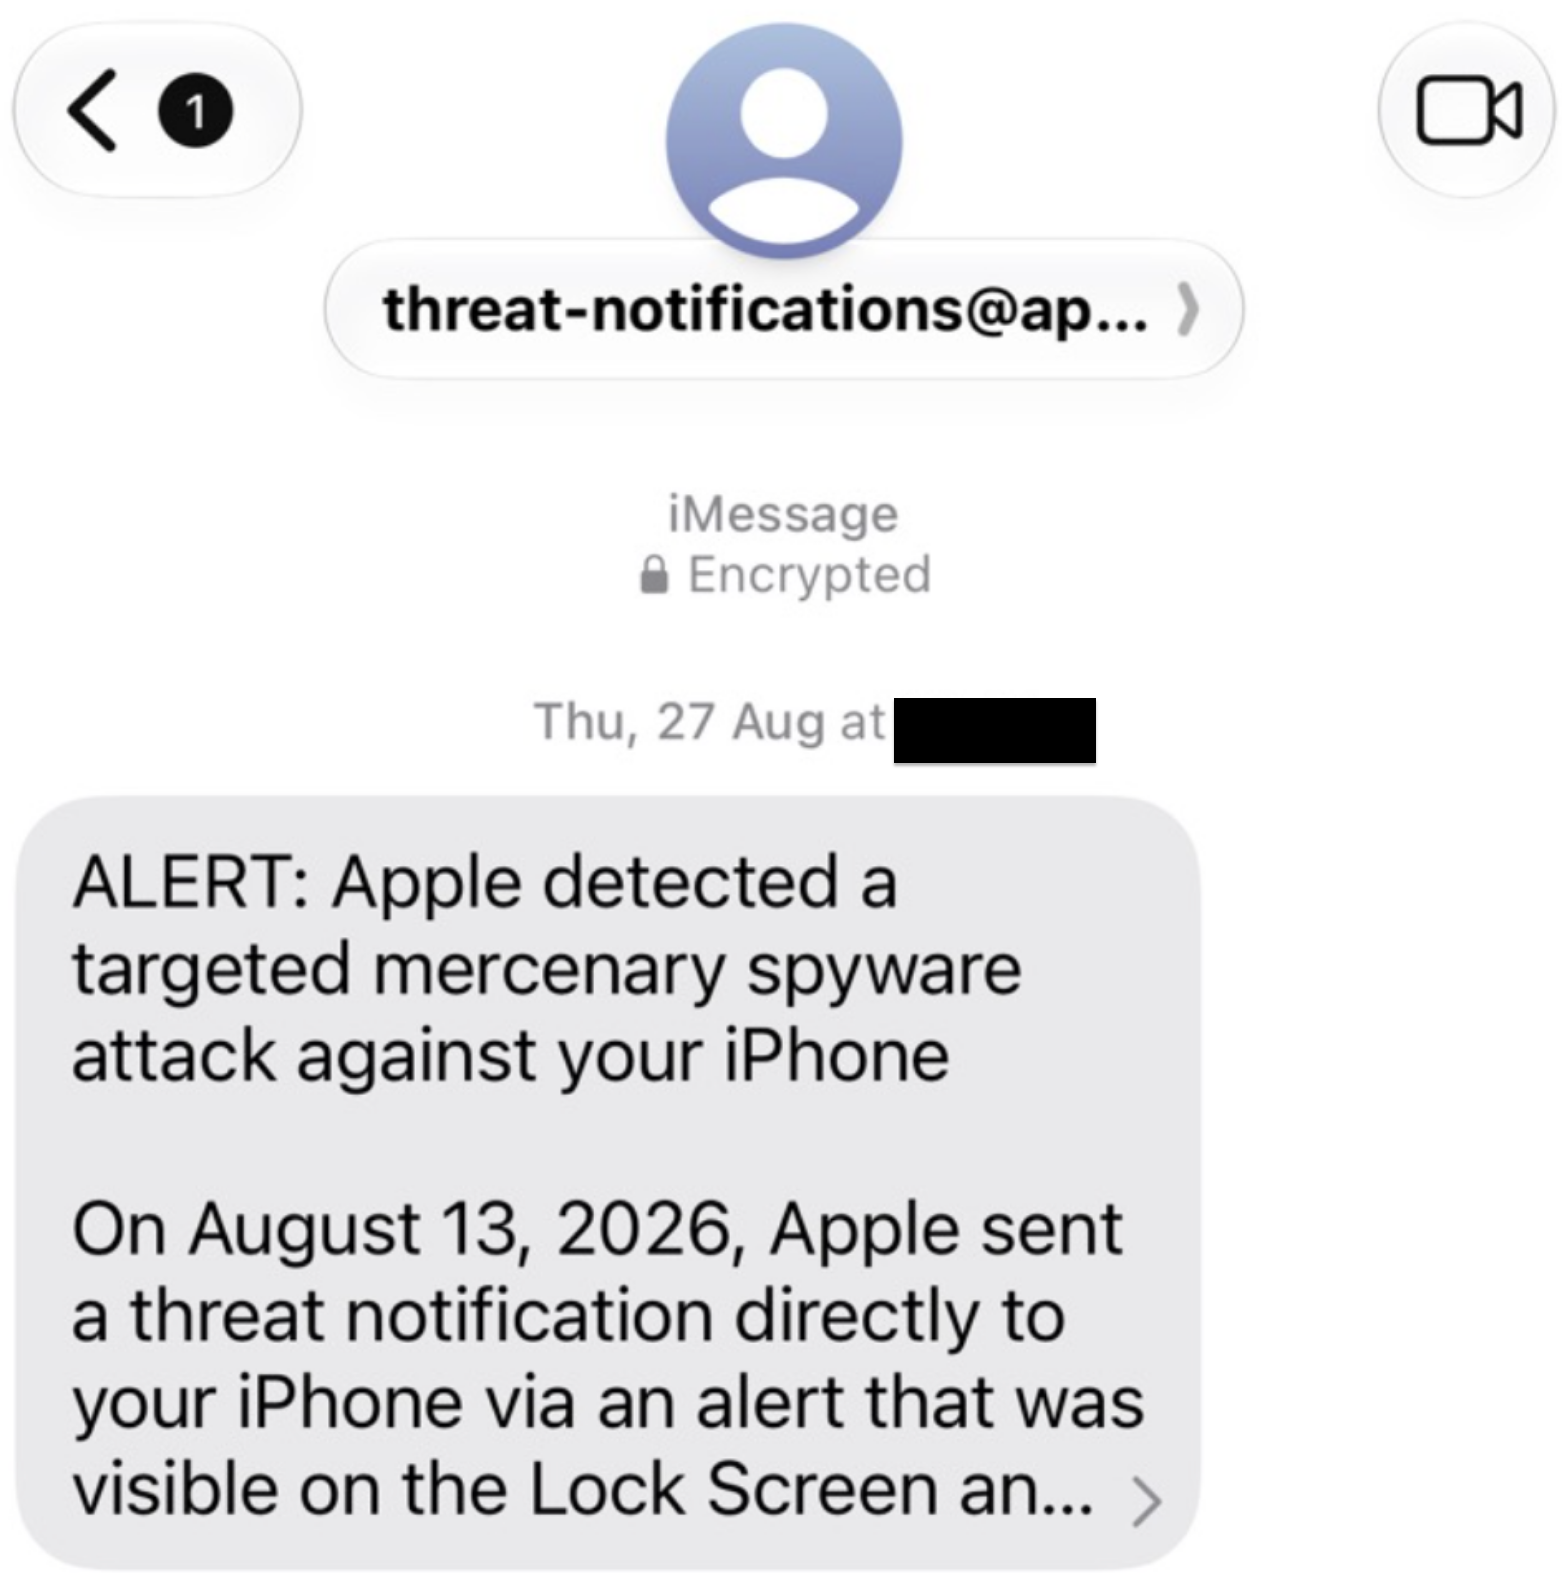
We judge the receipt of an Apple Threat Notification to be a high confidence indicator that his device was likely targeted with mercenary spyware, such as Pegasus.
Our forensic analysis of the artifacts collected from his device is ongoing.
Received an Apple Threat Notification? Take Action Now
This section has been adapted from this report.
An Apple Threat Notification is serious, and indicates that you were likely targeted by a government using mercenary spyware, such as Pegasus. We encourage you to consult this FAQ on Apple Threat Notifications by Access Now.
If you have received an Apple Threat Notification you should immediately seek expert assistance. Individuals in Serbia that received a notification should get in touch with The SHARE Foundation. We also recommend that recipients of Apple Threat Notifications ensure that close contacts such as family members and collaborators also seek spyware screening.
If you are not in Serbia, but received an Apple Threat Notification, we encourage you to immediately contact trusted experts, such as Access Now’s Digital Security Helpline, which supports members of civil society like human rights defenders, journalists, and dissidents.
At Risk? Use Lockdown Mode on your iPhone
If you believe that you may be targeted with mercenary spyware because of who you are or what you do, we urge you to use optional security features on your iPhone. Apple users can enable Lockdown Mode, which seriously increases the security of your device.
Click HERE for instructions on how to enable Apple’s Lockdown Mode
If you think you may be at risk from mercenary spyware, we encourage you to consult a trusted digital security expert for assistance. There is no substitute for personalized digital security advice, however, you may also find online security resources such as the Security Planner helpful.
Keep Your iPhone Updated!
We urge everyone, especially those facing increased risks because of who they are or the work they do, to keep all devices updated.
Click HERE for instructions on how to keep your iPhone up to date.
Acknowledgements
The Citizen Lab would like to thank the individuals mentioned in this note for allowing us to analyze their cases, and write about them. Without the participation of civil society and spyware targets, such research would be impossible.
We thank the team at the SHARE Foundation for their collaboration in this investigation.
We thank our colleagues Adam Senft and Maia Scott for editorial assistance and review, and special thanks to the Citizen Lab’s technical staff for additional assistance.
Special thanks to TNG.